


 Home
AI Community Alarmed as litellm Library Hit in Software Supply Chain Attack
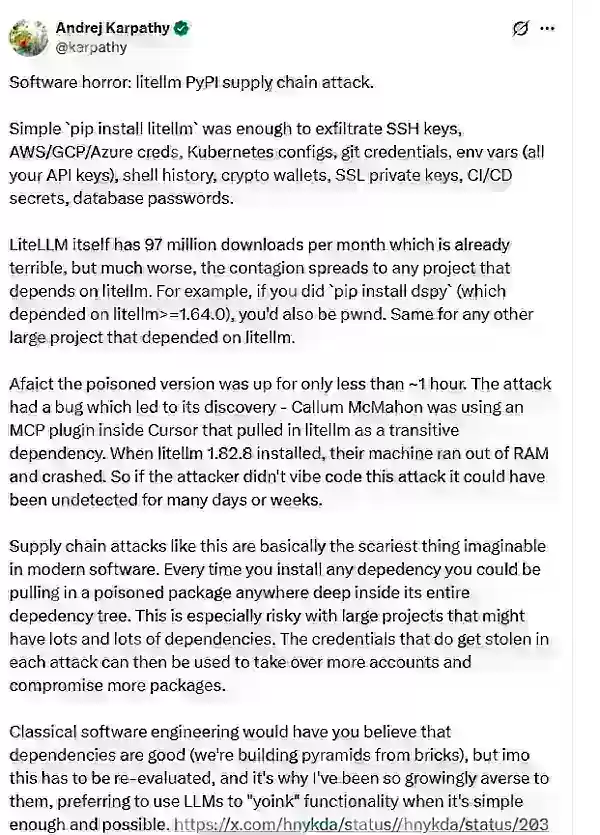
The AI developer community has been shaken by a recent alert from renowned AI scientist Andrej Karpathy, revealing a targeted poisoning attack on the AI software supply chain. The target is the popular Python library litellm, which boasts over 40,000 GitHub stars and nearly 100 million monthly downloads. As a universal adapter for calling major AI model APIs, the library's compromise has triggered a domino effect, potentially impacting the entire AI development toolchain.
Infected Upon Installation: The "Invisible" Operation of Malicious Code
The attack's stealth stems from its clever trigger. Malicious actors inserted a rogue .pth file into two specific PyPI releases of litellm (versions 1.82.7 and 1.82.8).
Automatic Execution: Simply installing either of these compromised versions via pip install causes the malicious code to run automatically with every Python process start. No manual import or function call is needed—your system is exposed the moment installation completes.
Comprehensive Data Exfiltration: Once active, the code aggressively harvests a wide range of sensitive host data. This includes SSH keys, cloud credentials (AWS/GCP), Kubernetes keys, cryptocurrency wallets, and all environment variables—which often contain valuable large model API keys. The stolen information is encrypted and transmitted to the attacker's remote server.
An Unexpected Twist: The Attacker Exposed by a "Bug"
This potentially long-undetected crime was foiled by the hacker's own mistake. A developer noticed their machine's memory usage suddenly spiking while using an extension in the Cursor editor.
Investigation revealed the malicious code triggered a process fork bomb—an exponential replication that quickly crashed the system. This instability became the critical clue that allowed security researchers to trace the issue back to the poisoned package. Karpathy noted that had the attacker's code been more competently written, this large-scale theft might still be ongoing.
Chain Reaction: How Security Tools Became the "Knife Carrier"
The incident highlights a cascade of supply chain failures. The attacker group, TeamPCP, first compromised the security scanning tool Trivy. Using stolen credentials, they obtained litellm 's release token, bypassed code review, and uploaded the malicious package directly to PyPI.
The fallout is extensive. Over 2,000 widely-used AI tools, including DSPy, MLflow, and Open Interpreter, rely indirectly on this library. Security experts urgently advise developers to check their installations by running pip show litellm. If the version is 1.82.7 or higher, assume complete credential leakage and immediately rotate all sensitive keys and tokens.
Related article
 Suno to Watermark Songs Amid Legal Battles
Suno, the platform enabling users to generate AI-created music, has unveiled new features to label platform-produced tracks, restrict downloads, and update community standards to curb unauthorized replicas. These updates arrive as Suno confronts mult
Musk Admits Grok Build Leaked User Code, Promises to Erase All Historical Data
Elon Musk directly addressed the privacy controversy surrounding Grok Build, beginning with a simple "True" to confirm the incident's validity. He pledged that all user data previously uploaded to SpaceXAI would be permanently erased, stating, "not a
U.S. Stocks Hit Historic Milestone as AI and Aerospace Giants Prepare for Trillion-Dollar Debut
Elon Musk, Sam Altman, and Dario Amodei, three titans of the technology sector, are advancing toward initial public offerings for their respective ventures. With SpaceX, OpenAI, and Anthropic—three industry behemoths nearing trillion-dollar valuation
Related Special Topic Recommendations
SEO
 Best AI SERP Analysis Tools for Search Strategy
2026 Latest Best Top-rated AI SERP Analysis Tools for Search Strategy are curated by XIX.AI through rigorous real-world tests and weekly updated rankings. These powerful tools help you unlock hidden optimization opportunities, boost content performance, and gain a competitive edge in search. Discover your perfect tool to elevate your search strategy today. Explore now!
 13 tools
 xix.ai
Data Analysis
Best AI Anomaly Detection Tools for KPI Monitoring across SaaS and Ecommerce Teams
2026 Latest Best Top-rated AI Anomaly Detection Tools for KPI Monitoring in SaaS and Ecommerce teams! XIX.AI has curated a powerful, game-changing collection based on rigorous real-world tests and weekly updated rankings. You’ll find detailed free vs paid comparison insights to help you identify the must-try solution that boosts productivity and unlocks your AI edge. Explore now!
10 tools
xix.ai
writing
Best AI Outline Generators for Long-Form SEO Articles
2026 Latest Best Top-Rated AI Outline Generators for Long-Form SEO Articles, meticulously curated by XIX.AI. These powerful tools offer game-changing assistance in creating high-quality content quickly, boosting writing efficiency significantly. Get a free vs paid comparison along with real-world tests and detailed rankings to help you find the must-try option that suits your needs. Explore now to unlock your AI edge.
8 tools
xix.ai
Education and Learning
AI Study Tools for Homework and Exam Prep
2026 Latest Best AI Study Tools for Homework and Exam Prep! XIX.AI curates a top-rated list of powerful, game-changing tools that help students boost productivity, streamline homework completion, and ace exams through real-world tests. Get a free vs paid comparison, detailed rankings, and must-try options to unlock your AI edge. Explore now!
10 tools
xix.ai
Music composition
AI Vocal Demo Tools for Songwriters, Hooks, Toplines, and Multilingual Draft Sessions
2026 Latest Best AI Vocal Demo Tools for Songwriters, Hook Creators, and Multi-Language Content Teams! XIX.AI has curated a top-rated list of powerful game-changing tools that go through rigorous real-world tests. You’ll find detailed free vs paid comparison data, comprehensive rankings, and must-try options to help you boost writing efficiency and unlock your creative potential. Explore now to discover your perfect tool for all your content needs!
9 tools
xix.ai
Business
Best AI Competitive Research Tools for Small Businesses
2026 Latest Best Top-rated AI Competitive Research Tools for Small Businesses! XIX.AI has curated a highly powerful game-changing collection, updated weekly with rigorous real-world tests and detailed rankings. You can find a comprehensive free vs paid comparison to help you identify the must-try tools that boost your productivity and give you a competitive edge. Explore now to discover your perfect tool!
9 tools
xix.ai

 Comments (0)
0/500
The AI developer community has been shaken by a recent alert from renowned AI scientist Andrej Karpathy, revealing a targeted poisoning attack on the AI software supply chain. The target is the popular Python library litellm, which boasts over 40,000 GitHub stars and nearly 100 million monthly downloads. As a universal adapter for calling major AI model APIs, the library's compromise has triggered a domino effect, potentially impacting the entire AI development toolchain.
Infected Upon Installation: The "Invisible" Operation of Malicious Code
The attack's stealth stems from its clever trigger. Malicious actors inserted a rogue .pth file into two specific PyPI releases of
Automatic Execution: Simply installing either of these compromised versions via pip install causes the malicious code to run automatically with every Python process start. No manual import or function call is needed—your system is exposed the moment installation completes.
Comprehensive Data Exfiltration: Once active, the code aggressively harvests a wide range of sensitive host data. This includes SSH keys, cloud credentials (AWS/GCP), Kubernetes keys, cryptocurrency wallets, and all environment variables—which often contain valuable large model API keys. The stolen information is encrypted and transmitted to the attacker's remote server.
An Unexpected Twist: The Attacker Exposed by a "Bug"
This potentially long-undetected crime was foiled by the hacker's own mistake. A developer noticed their machine's memory usage suddenly spiking while using an extension in the Cursor editor.
Investigation revealed the malicious code triggered a process fork bomb—an exponential replication that quickly crashed the system. This instability became the critical clue that allowed security researchers to trace the issue back to the poisoned package. Karpathy noted that had the attacker's code been more competently written, this large-scale theft might still be ongoing.
Chain Reaction: How Security Tools Became the "Knife Carrier"
The incident highlights a cascade of supply chain failures. The attacker group, TeamPCP, first compromised the security scanning tool Trivy. Using stolen credentials, they obtained
The fallout is extensive. Over 2,000 widely-used AI tools, including DSPy, MLflow, and Open Interpreter, rely indirectly on this library. Security experts urgently advise developers to check their installations by running pip show litellm. If the version is 1.82.7 or higher, assume complete credential leakage and immediately rotate all sensitive keys and tokens.








 Suno to Watermark Songs Amid Legal Battles
Suno, the platform enabling users to generate AI-created music, has unveiled new features to label platform-produced tracks, restrict downloads, and update community standards to curb unauthorized replicas. These updates arrive as Suno confronts mult
 Musk Admits Grok Build Leaked User Code, Promises to Erase All Historical Data
Elon Musk directly addressed the privacy controversy surrounding Grok Build, beginning with a simple "True" to confirm the incident's validity. He pledged that all user data previously uploaded to SpaceXAI would be permanently erased, stating, "not a
 U.S. Stocks Hit Historic Milestone as AI and Aerospace Giants Prepare for Trillion-Dollar Debut
Elon Musk, Sam Altman, and Dario Amodei, three titans of the technology sector, are advancing toward initial public offerings for their respective ventures. With SpaceX, OpenAI, and Anthropic—three industry behemoths nearing trillion-dollar valuation

2026 Latest Best Top-rated AI SERP Analysis Tools for Search Strategy are curated by XIX.AI through rigorous real-world tests and weekly updated rankings. These powerful tools help you unlock hidden optimization opportunities, boost content performance, and gain a competitive edge in search. Discover your perfect tool to elevate your search strategy today. Explore now!
13 tools
xix.ai

2026 Latest Best Top-rated AI Anomaly Detection Tools for KPI Monitoring in SaaS and Ecommerce teams! XIX.AI has curated a powerful, game-changing collection based on rigorous real-world tests and weekly updated rankings. You’ll find detailed free vs paid comparison insights to help you identify the must-try solution that boosts productivity and unlocks your AI edge. Explore now!
10 tools
xix.ai

2026 Latest Best Top-Rated AI Outline Generators for Long-Form SEO Articles, meticulously curated by XIX.AI. These powerful tools offer game-changing assistance in creating high-quality content quickly, boosting writing efficiency significantly. Get a free vs paid comparison along with real-world tests and detailed rankings to help you find the must-try option that suits your needs. Explore now to unlock your AI edge.
8 tools
xix.ai

2026 Latest Best AI Study Tools for Homework and Exam Prep! XIX.AI curates a top-rated list of powerful, game-changing tools that help students boost productivity, streamline homework completion, and ace exams through real-world tests. Get a free vs paid comparison, detailed rankings, and must-try options to unlock your AI edge. Explore now!
10 tools
xix.ai

2026 Latest Best AI Vocal Demo Tools for Songwriters, Hook Creators, and Multi-Language Content Teams! XIX.AI has curated a top-rated list of powerful game-changing tools that go through rigorous real-world tests. You’ll find detailed free vs paid comparison data, comprehensive rankings, and must-try options to help you boost writing efficiency and unlock your creative potential. Explore now to discover your perfect tool for all your content needs!
9 tools
xix.ai

2026 Latest Best Top-rated AI Competitive Research Tools for Small Businesses! XIX.AI has curated a highly powerful game-changing collection, updated weekly with rigorous real-world tests and detailed rankings. You can find a comprehensive free vs paid comparison to help you identify the must-try tools that boost your productivity and give you a competitive edge. Explore now to discover your perfect tool!
9 tools
xix.ai












